Useful notes on security, AI and technology.
I write to document what I learn from cybersecurity, AI security research and practical technology work. The goal is to make technical ideas useful to people, not to publish content simply for search engines.
Areas I intend to build deeper content around.
These topics reflect my professional and research interests and provide a clear structure for future writing.
Recent writing.
Browse the latest articles as visual cards. Filter by category, then open any article for the full explanation, diagrams, examples and references.
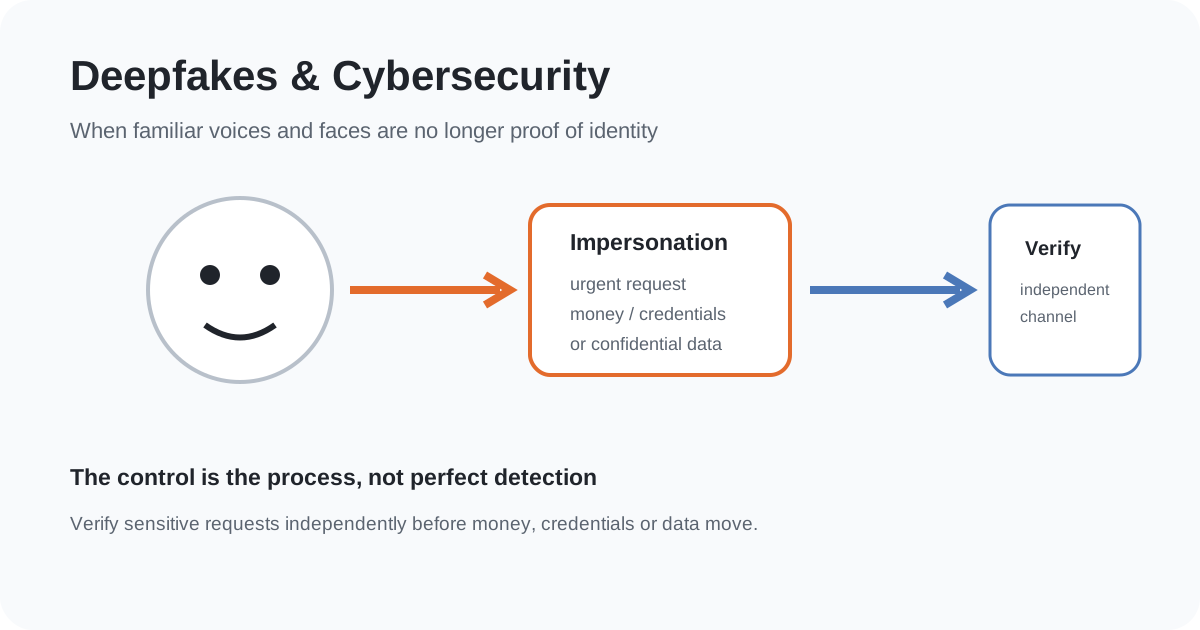
Deepfakes and Cybersecurity: How AI-Generated Voice and Video Are Used in Fraud
Learn how AI-generated voice and video can support impersonation scams, why detection is difficult, and how people and organisations can verify high-risk requests.
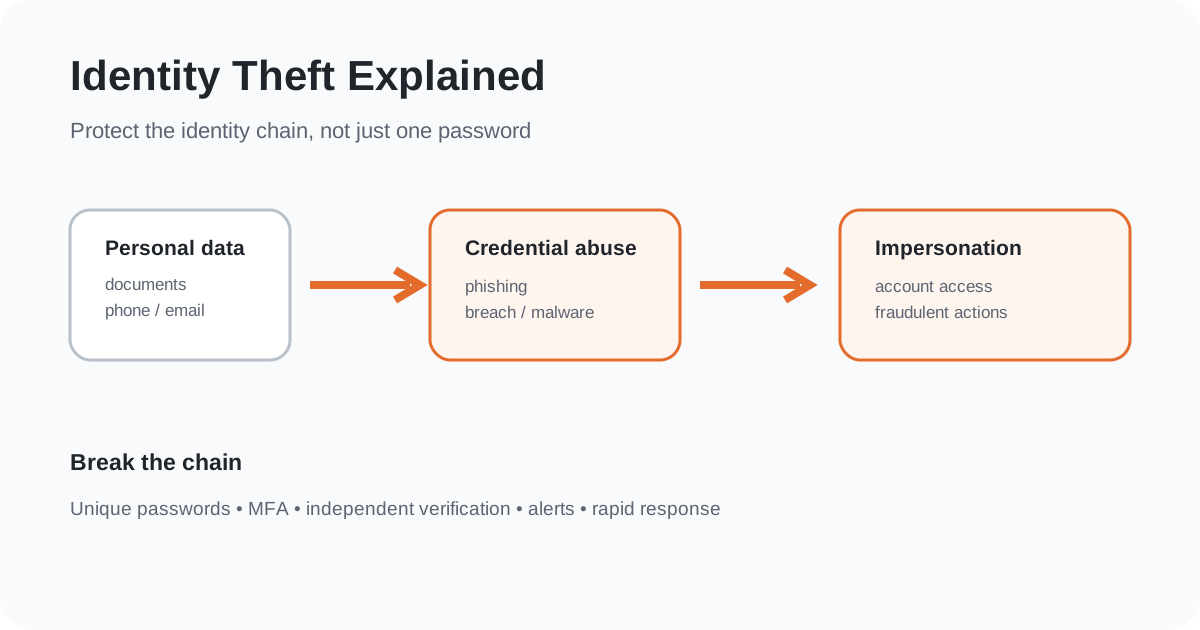
Identity Theft Explained: How It Happens and How to Protect Yourself
Learn what identity theft actually means, how stolen personal information is abused, and the practical steps that reduce identity and account takeover risk.
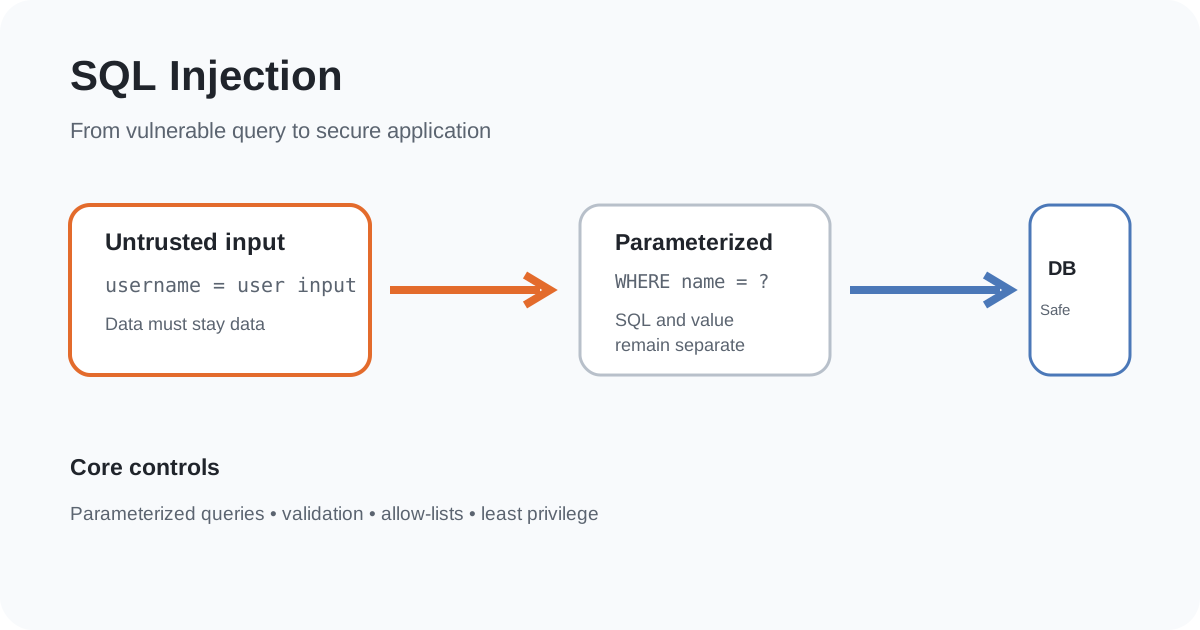
SQL Injection Explained: From Vulnerable Query to Secure Application
Understand how SQL injection happens, why string concatenation is dangerous, and how parameterized queries, validation and least privilege protect applications.
Authenticator App vs SMS OTP: Which Is More Secure?
Compare authenticator apps and SMS one-time passwords, understand their risks, and choose a stronger MFA method for important accounts.
How Passwords Are Cracked and What Actually Makes a Password Strong
Learn how attackers guess, reuse and crack passwords, why length and uniqueness matter, and what modern password guidance recommends.
Tool Poisoning in AI Agents: How Trusted Tools Can Become an Attack Path
Understand how AI agent tools can be poisoned, manipulated or misused, and how to design safer tool-integrated agent systems.
AI Agent Memory Poisoning: Can an Attacker Manipulate What an Agent Remembers?
Learn how memory and persistent context can become an attack surface for AI agents, and how to validate, isolate and control stored context.
API Security Explained: How Modern APIs Are Attacked and Protected
A practical introduction to API security, including authorization, authentication, data exposure, rate limits, inventory and third-party API risks.
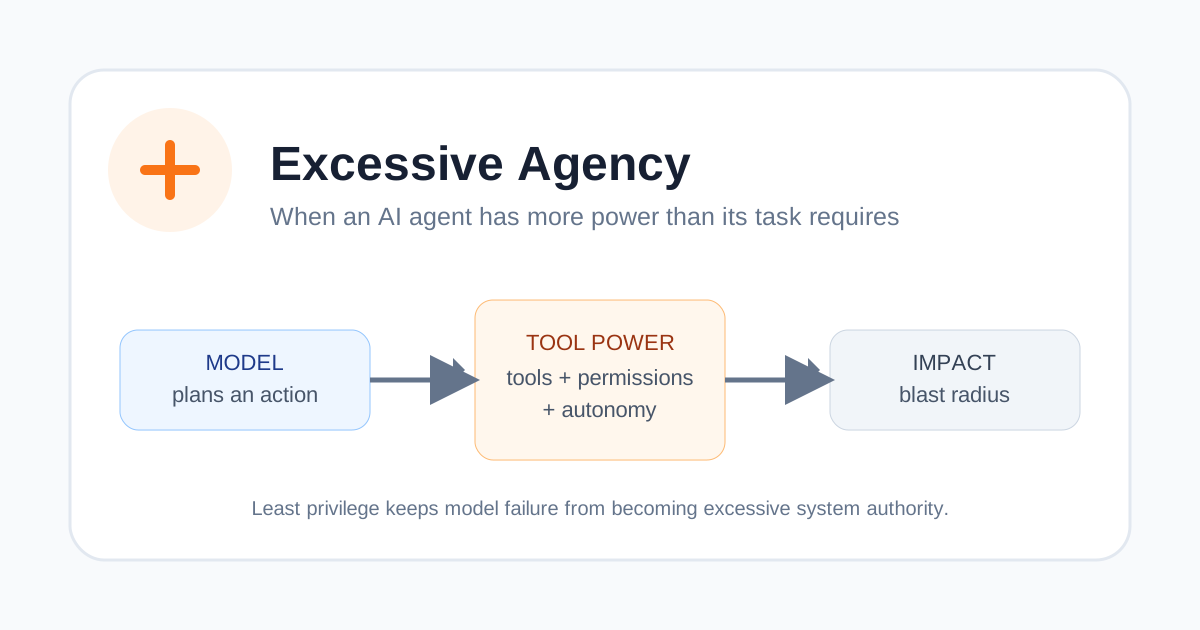
Excessive Agency in AI Systems: When an AI Agent Has Too Much Power
Learn what excessive agency means in AI systems, why too many tools or permissions increase risk, and how to design safer agent boundaries.
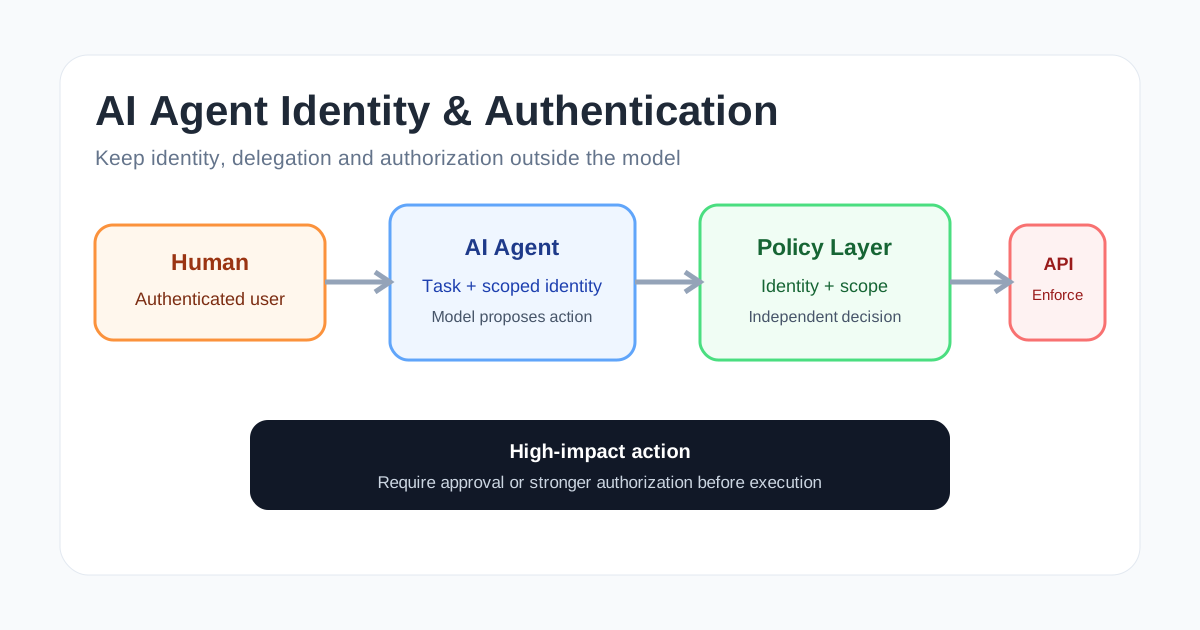
AI Agent Identity and Authentication: Who Is Actually Performing the Action?
Understand how AI agents should be identified, authenticated and authorized when they act on behalf of people or other software.
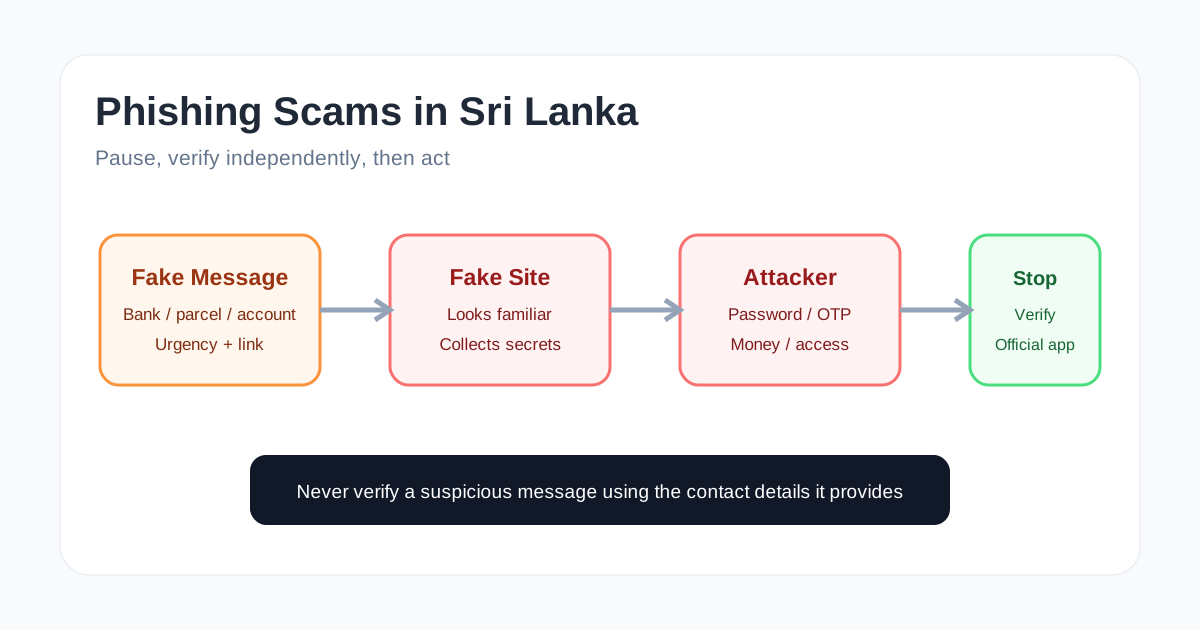
Phishing Scams in Sri Lanka: How to Recognise Fake Bank and Account Messages
A practical Sri Lankan guide to spotting fake bank, parcel, account and payment messages before they steal passwords, OTPs or money.
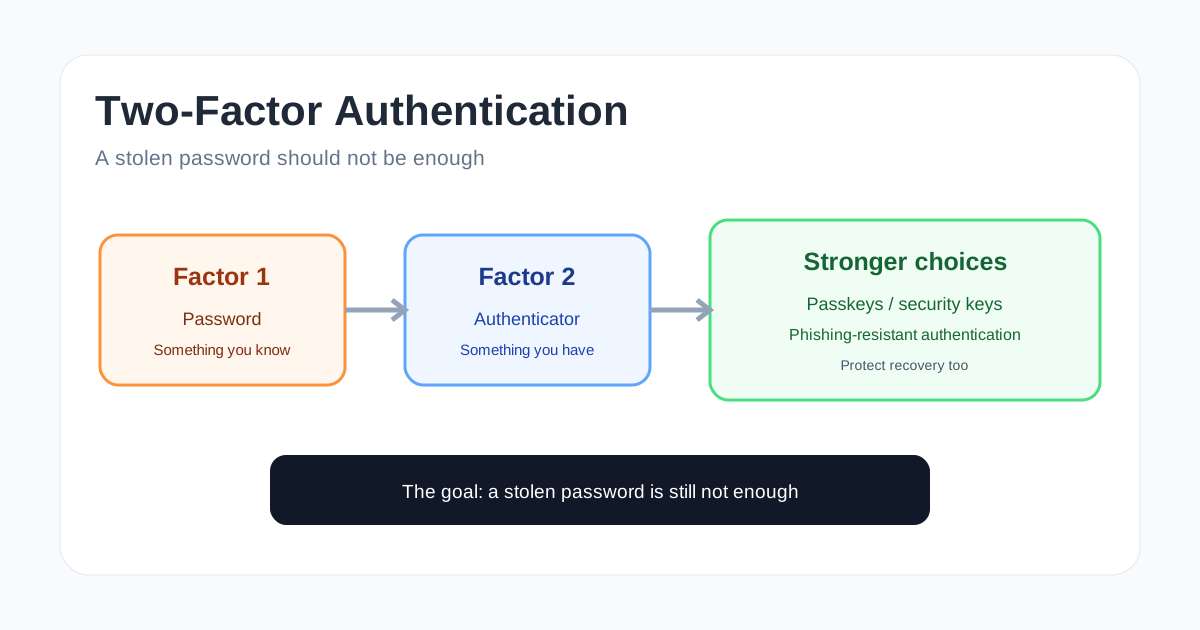
Two-Factor Authentication Explained: Why a Password Alone Is Not Enough
Learn how two-factor authentication works, why different MFA methods have different strengths, and how to choose a safer second factor.
Authentication Failures: Common Login Security Mistakes
A practical guide to authentication failures, including weak passwords, account enumeration, session mistakes, recovery flaws and missing phishing-resistant controls.
Least Privilege for AI Agents: Why an AI System Should Not Have Access to Everything
Learn how least privilege limits AI agents, reduces the impact of prompt injection and mistakes, and turns broad tool access into controlled permissions.
Passkeys vs Passwords: Are Passkeys Really More Secure?
A practical guide to passkeys, passwords, phishing resistance, recovery and the trade-offs to understand before switching your accounts.
How to Become a Penetration Tester: A Practical Learning Roadmap
A practical roadmap for becoming a penetration tester, from networking and operating systems to web security, labs, reporting, portfolios and professional growth.
Shadow AI Explained: The Security Risk of Unapproved AI Tools at Work
A practical guide to shadow AI, why unapproved AI tools create security and governance gaps, and how organisations can reduce risk without blocking useful innovation.
Injection Attacks Explained: SQL Injection, Command Injection and More
Learn how injection vulnerabilities happen when untrusted data crosses into an interpreter, with practical SQL, command, NoSQL and other examples plus secure design guidance.
AI Coding Assistants and Security: What Developers Should Check Before Trusting Generated Code
A practical security guide for reviewing AI-generated code, dependencies, data flows and permissions before generated suggestions reach production.
Password Managers Explained: Are They Actually Safe?
A practical explanation of how password managers protect credentials, what risks they introduce, and how to choose and secure one properly.
How to Build a Secure AI Chatbot: A Practical Security Checklist
A practical defense-in-depth guide to securing AI chatbots across identity, prompts, data, model output, tools, logging and testing.
What Should You Do After Your Data Appears in a Data Breach?
A practical step-by-step guide to responding after your personal data appears in a breach, including passwords, payment details, identity data and account recovery.
Cryptographic Failures Explained: Encryption Mistakes Developers Still Make
Understand common cryptographic failures, from weak algorithms and nonce reuse to poor key management, password storage and TLS mistakes, with practical developer guidance.
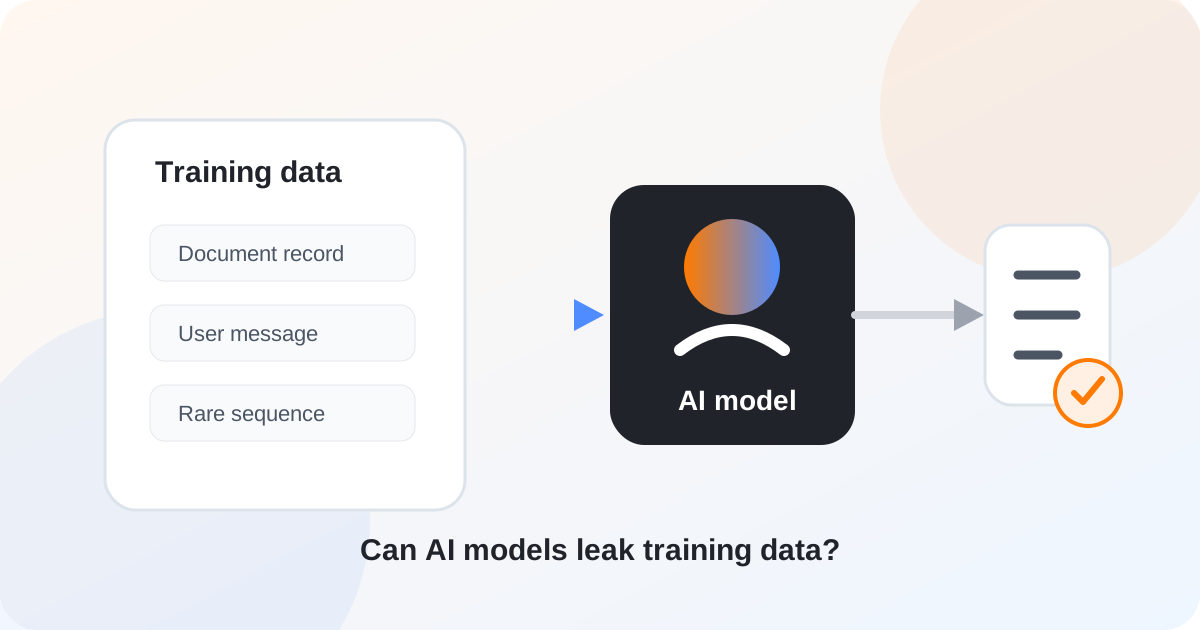
Can AI Models Leak Training Data? Understanding Memorisation and Data Exposure
Learn how AI models can memorise and expose training data, how training data extraction differs from ordinary model output, and how teams can reduce privacy risk.
AI Supply Chain Security: Risks in Models, Libraries, Plugins and Data
Understand AI supply chain security across models, libraries, plugins, datasets and deployment systems, with practical controls for verifying what your AI application trusts.
What Should You Do If One of Your Online Accounts Gets Hacked?
A practical recovery guide for a hacked online account, including how to regain control, remove attacker access, protect connected accounts, and reduce the chance of another takeover.
Software Supply Chain Attacks: How Trusted Dependencies Become a Security Risk
Learn how software supply chain attacks compromise dependencies, build systems and release pipelines, plus practical controls for reducing the risk.
Data Poisoning in AI: How Training Data and Knowledge Sources Can Be Manipulated
Understand AI data poisoning across training, fine-tuning and retrieval systems, how it differs from prompt injection, and how to reduce the risk.
How to Report a Cybersecurity Incident in Sri Lanka
A practical guide to reporting cybersecurity incidents in Sri Lanka, including when to contact Sri Lanka CERT, when police involvement matters, and what evidence to preserve.
How to Tell If Your Email Account Has Been Hacked
Learn the strongest signs of email account compromise, what to check first, and how to recover and secure your account without relying on guesswork.
Jailbreaking vs Prompt Injection: What Is the Difference?
Understand the difference between AI jailbreaking and prompt injection, how direct and indirect attacks fit together, and which controls reduce real application risk.
Security Misconfiguration: Common Examples and How to Prevent Them
Understand security misconfiguration, common examples across applications and cloud systems, and practical ways to prevent configuration mistakes.
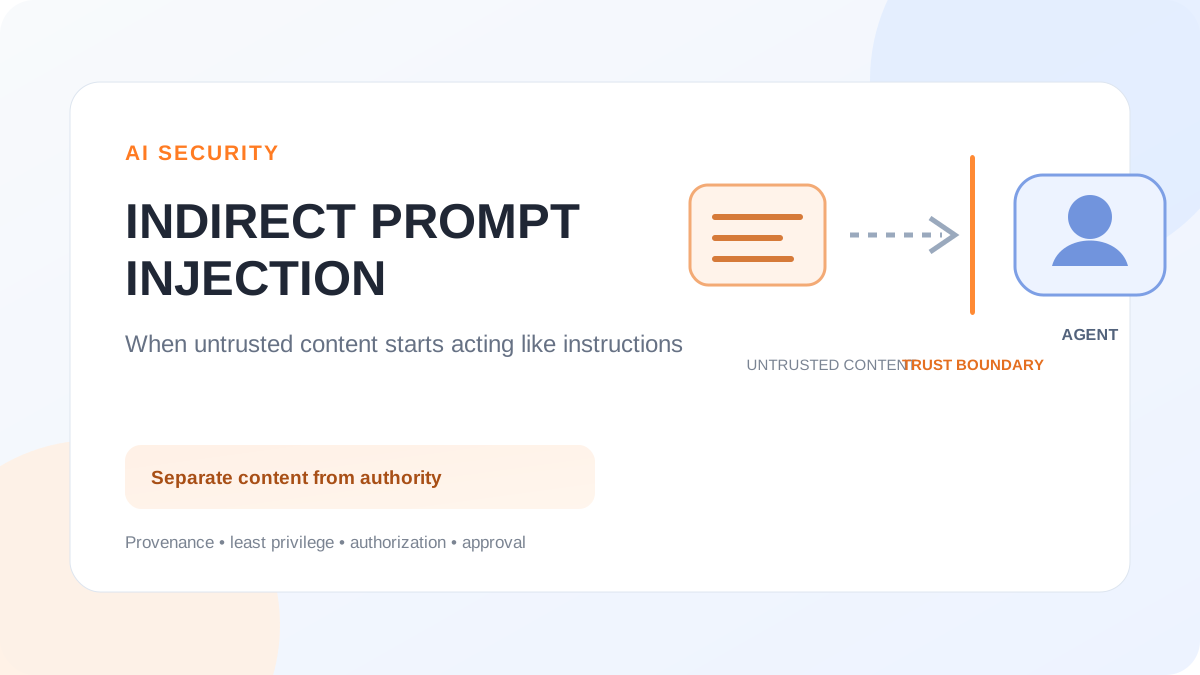
Indirect Prompt Injection: How Malicious Content Can Hijack an AI Agent
Learn how indirect prompt injection reaches AI systems through webpages, documents, email, RAG data and tools, and how to contain the resulting security risk.
How to Tell If Your Phone Has Been Hacked
Learn which signs really suggest a phone may be compromised, which symptoms are weak clues, and what to check on Android and iPhone before taking action.
What Is AI Red Teaming? How Security Testing for AI Systems Actually Works
Learn what AI red teaming tests, how it differs from ordinary security testing, and how to run a practical risk-based assessment of AI systems.
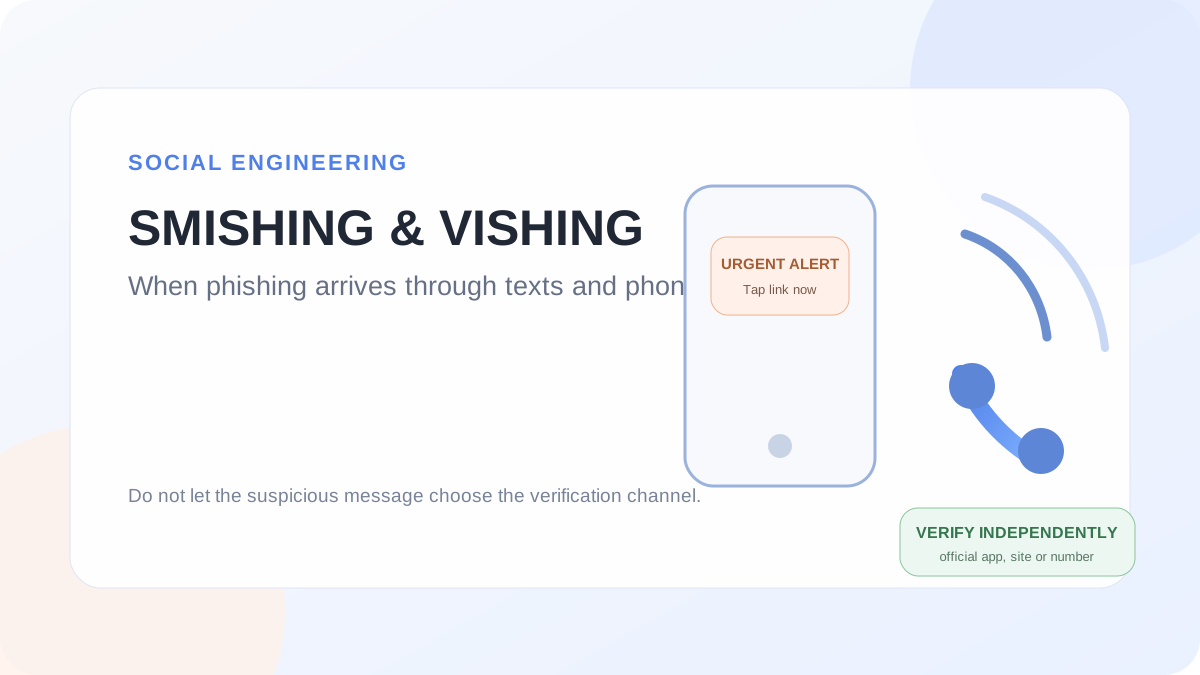
Smishing and Vishing Explained: When Phishing Comes Through SMS and Phone Calls
Learn how smishing and vishing work, why text and voice scams feel convincing, how to verify suspicious messages safely, and what to do after interacting with one.
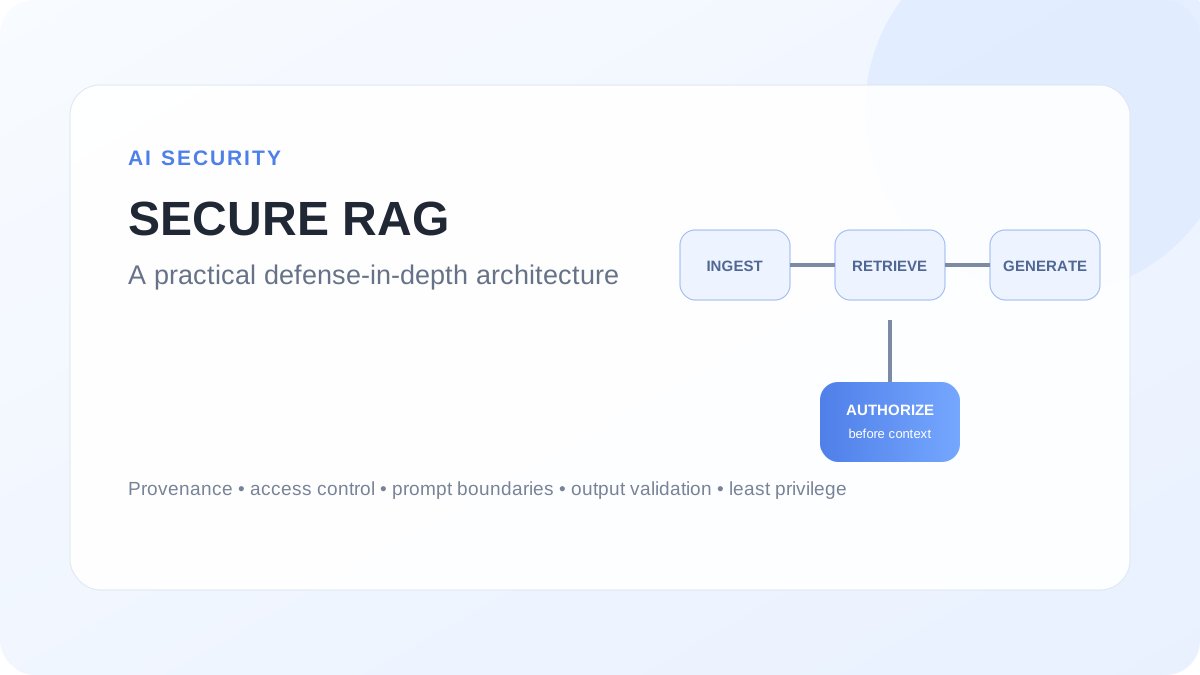
How to Secure a RAG Application: A Practical Architecture and Security Checklist
A practical defense-in-depth architecture for securing RAG applications across ingestion, vector storage, retrieval, prompts, outputs and tools.
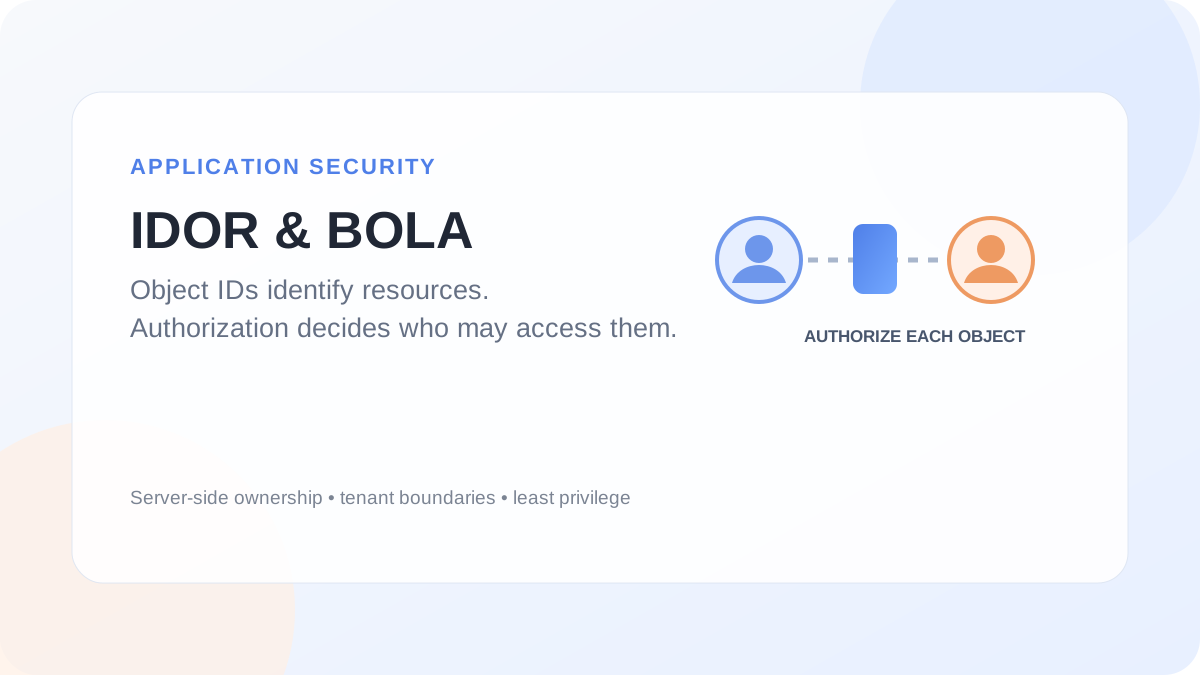
IDOR and BOLA Explained: How Applications Accidentally Expose Other Users' Data
Understand IDOR and BOLA, why object IDs are not the real problem, how authorization failures expose other users' data, and how to prevent them.
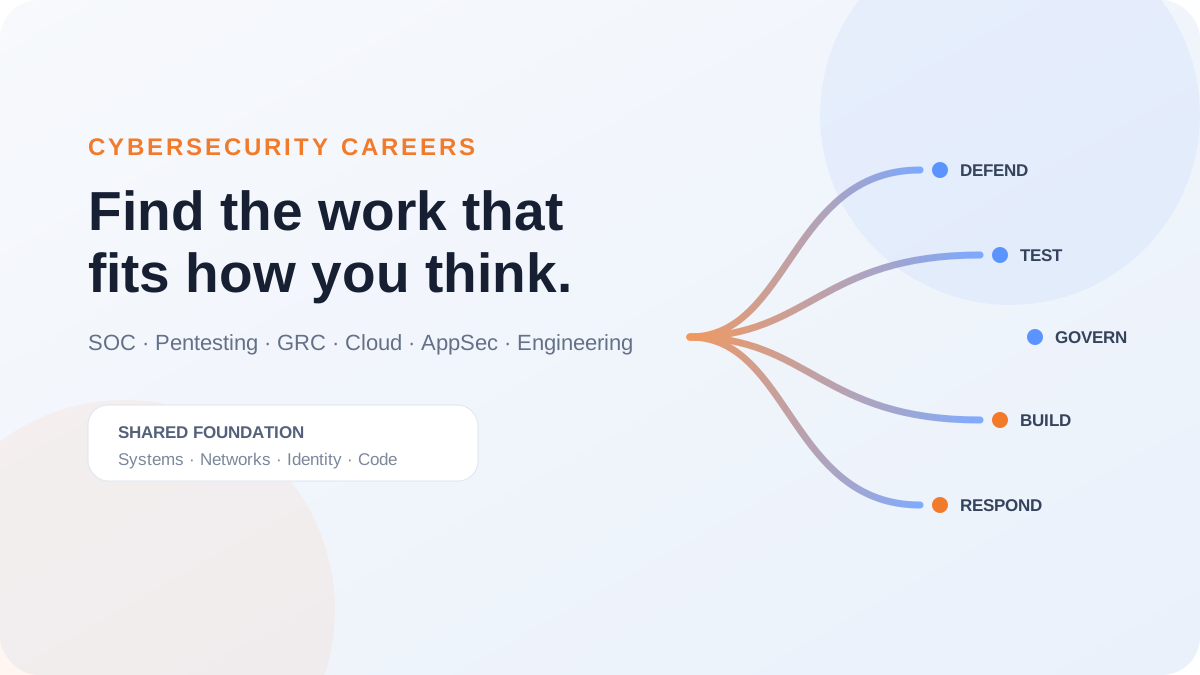
Cybersecurity Career Paths Explained: SOC, Pentesting, GRC, Cloud Security and More
A practical guide to cybersecurity career paths, what the work actually involves, the skills each path rewards, and how to choose a direction without guessing.
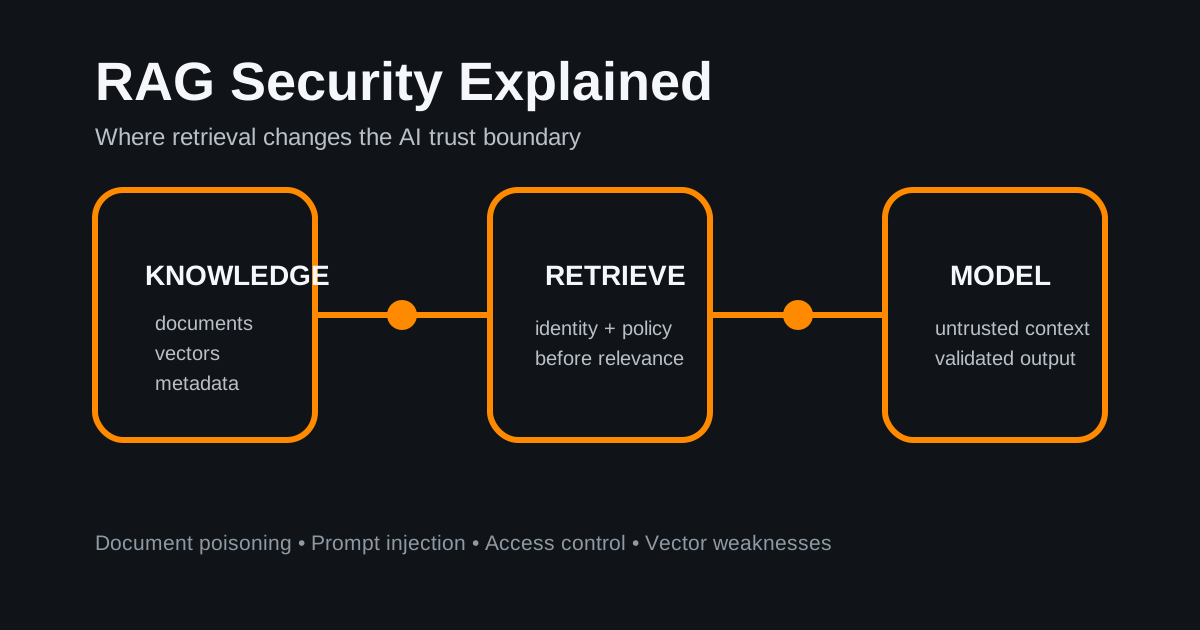
RAG Security Explained: How Retrieval-Augmented Generation Can Be Attacked
A practical security guide to RAG systems, covering document poisoning, indirect prompt injection, vector weaknesses, access-control failures and safer retrieval design.
What Is Phishing? How to Recognise a Phishing Email Before You Click
Learn how phishing works, the warning signs that matter, how to verify suspicious messages safely, and what to do if you already clicked or entered information.
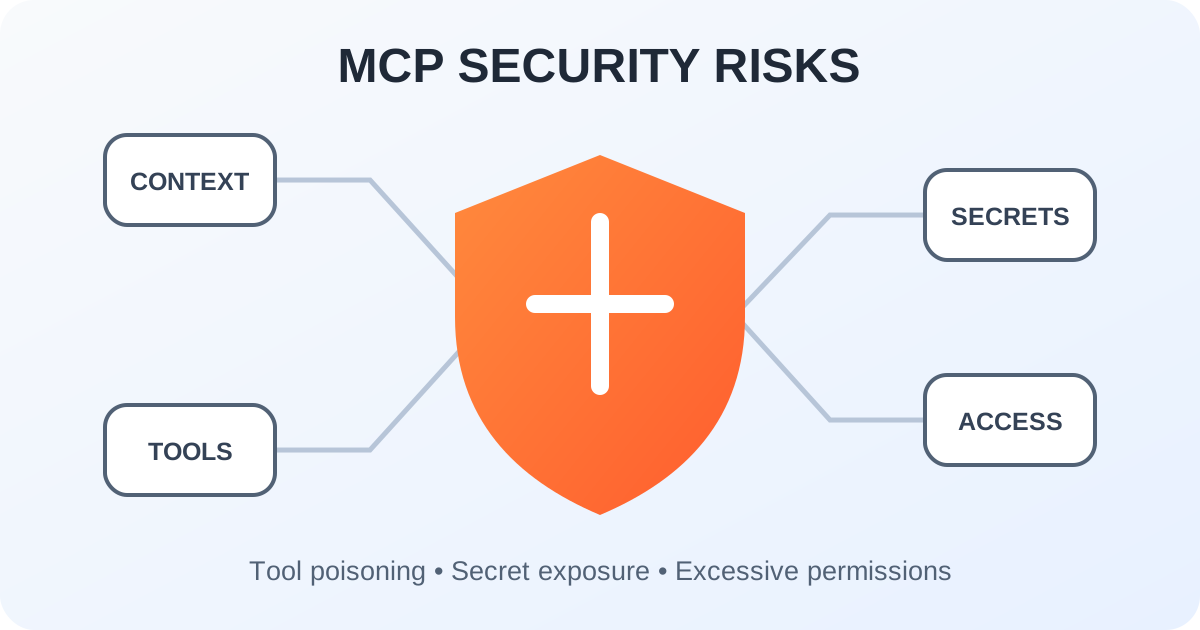
MCP Security Risks: Tool Poisoning, Secret Exposure and Excessive Permissions
A practical threat model for Model Context Protocol deployments, covering tool poisoning, secret exposure, excessive permissions and controls that reduce the blast radius.
Broken Access Control Explained: Why It Is the Number One OWASP Risk
Understand broken access control, how authorization failures expose data and functions, and how to design server-side controls that fail safely.
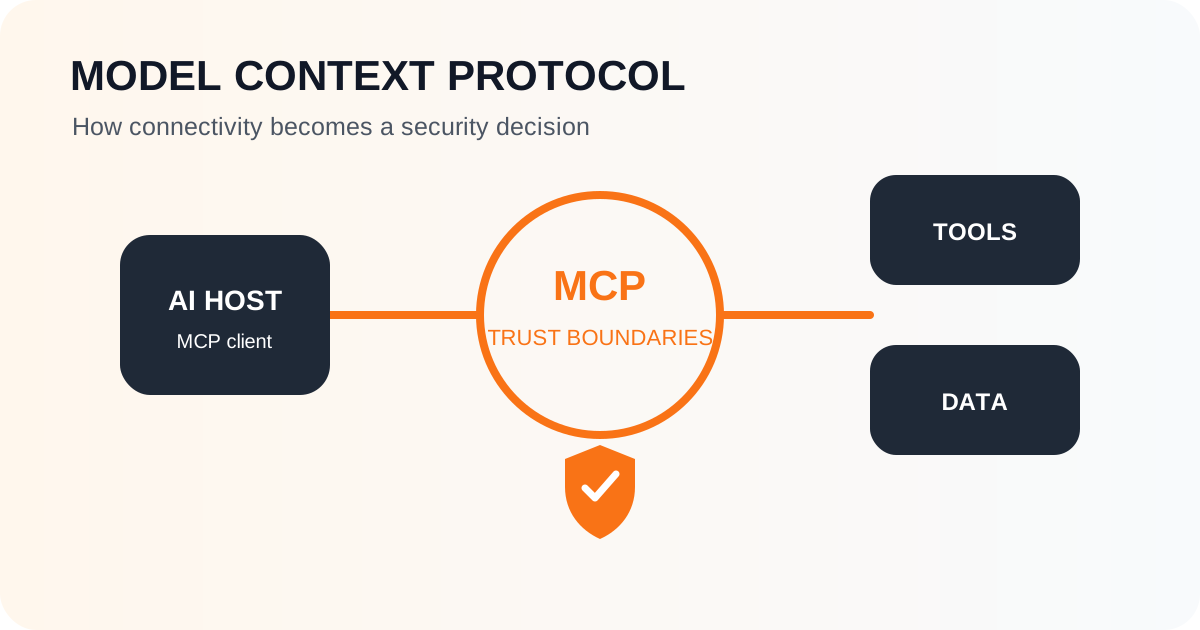
What Is Model Context Protocol (MCP) and Why Does MCP Security Matter?
A practical explanation of Model Context Protocol, how MCP connects AI applications to tools and data, and the security boundaries that matter in real deployments.
What Is Ransomware and How Does a Ransomware Attack Actually Work?
Understand how ransomware attacks develop from initial access to encryption and extortion, plus practical steps for prevention, response and recovery.
Sri Lanka's National Cyber Security Strategy 2025-2029 Explained
A practical explanation of Sri Lanka's National Cyber Security Strategy 2025-2029, its priorities, implementation direction and what it means for organisations and citizens.
OWASP Top 10 for Agentic AI Applications 2026: A Practical Security Guide
A practical guide to the OWASP Top 10 for Agentic Applications 2026, with realistic examples, architectural controls and secure design guidance for AI agents.
OWASP Top 10:2025 Explained with Practical Examples
A practical guide to the OWASP Top 10:2025, what changed from 2021, how each web application security risk appears, and how to reduce it.
What Is Malware? Viruses, Trojans, Worms, Spyware and Ransomware Explained
Understand what malware is, how viruses, worms, Trojans, spyware and ransomware differ, how infections happen, and what to do if you suspect one.
OWASP Top 10 for LLM Applications 2026 Explained with Practical Examples
A practical guide to the OWASP LLM Top 10 2026, what changed, how the risks connect, and how to design safer AI applications around them.
What Is AI Security? A Practical Guide to Risks and Protection in 2026
AI security explained in practical terms: prompt injection, data exposure, model and agent risks, and the controls that help reduce them.
Prompt Injection Explained: How AI Systems Can Be Manipulated and How to Defend Them
A practical explanation of prompt injection, direct and indirect attacks, why they matter, and the layered controls that reduce the risk.
Cybersecurity in Sri Lanka: Skills, Careers and What Beginners Should Learn
A practical guide for students and beginners in Sri Lanka who want to build real cybersecurity skills and understand the different career paths.
AI Agents and Cybersecurity: New Security Risks Organizations Need to Understand
AI agents can read data, use tools and take actions. This guide explains the main security risks and practical controls organizations should consider.
How to Protect Sensitive Data, API Keys and Credentials When Using AI Tools
Practical steps for protecting personal data, company information, API keys, passwords and other credentials when using AI tools and LLM applications.
Cybersecurity vs Information Security: Differences, Careers and Real-World Examples
Cybersecurity and information security overlap, but they are not exactly the same. This guide explains the difference with practical examples and career context.
Some writing will also be for students and parents.
ICT education articles will cover practical learning, O/L and A/L preparation, online learning and ways to understand technology beyond examination questions.
Explore ICT classes